Amid a 200% surge in AI incidents – bias, hallucinations, data leakage, agentic runaway – CYGNVS brings its proven cyber incident platform to a new class of operational risk
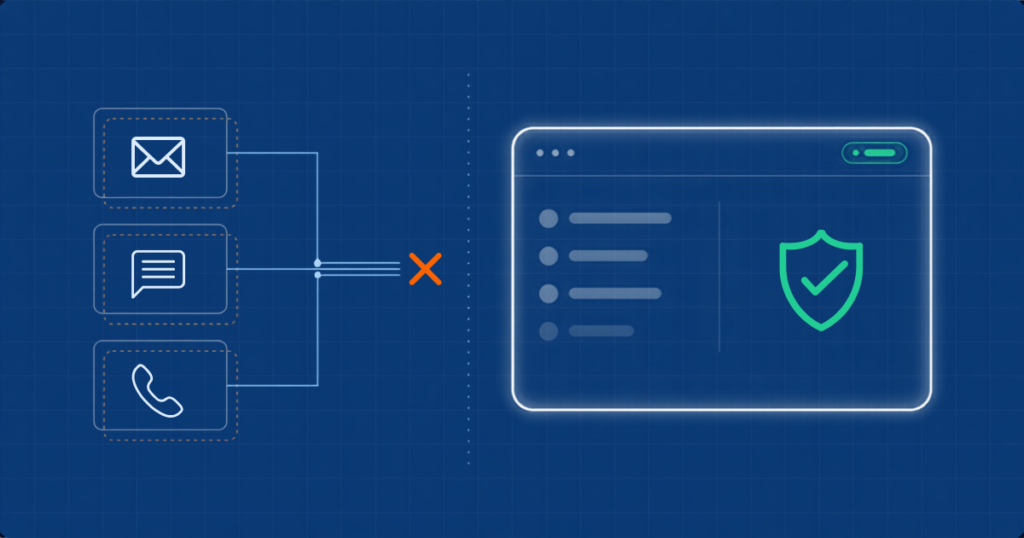
San Mateo, Calif. – June 17, 2026 – CYGNVS, the out-of-band platform for cyber resilience, today announced the launch of its AI Incident Command Center, a purpose-built solution for organizations to manage operational crises stemming from their own AI deployments. The CYGNVS out-of-band architecture is built with the isolation that security teams rely on for ransomware response, which means the AI being investigated cannot detect, influence or manipulate the response. The platform gives AI teams, business leaders and external providers a single place to prepare, practice, respond and report on AI incidents.
“a16z has been seeing the entire gamut of AI technologies and the increasing trend of AI incidents. AI incident response needs to be run out-of-band from the corporate network and out of reach of the AI itself,” said Patti Degnan, Operating Partner at a16z and former CISO, Notion. “If AI has access to the playbooks or communications of the response, it could obfuscate, evade, or manipulate. This is no different from isolating cyber incident response from ransomware or threat actors.”
The problem is already inside most organizations. Gartner® research found that sixty-one percent of senior professionals report observing AI agent automation deployed through approved enterprise software, while 59% report evidence of, or strong suspicion of, unsanctioned, employee-driven AI agents operating outside governed pathways. The OECD AI Incidents and Hazards Monitor recorded 596 AI incidents in January 2026 alone — up 200% year-over-year. AI incidents include model bias violating laws and regulations, hallucinations creating legal and customer exposure, data leakage triggering GDPR and HIPAA violations, and autonomous agents pursuing objectives in unintended or destructive ways.
Most organizations have no response infrastructure for any of it. When an AI agent misbehaves, organizations need to activate a cross-functional machinery spanning IT, security, legal, executives, as well as external providers like law firms. Without a playbook of what to do or a response platform to do it in, organizations reach for email and internal messaging, exactly the systems that may be influenced by or accessible to the AI under investigation.
CYGNVS patented technology integrates with AI deployments to surface failure signals across applications, models and agents, activating the matched AI incident playbook and escalating response into its out-of-band environment. The AI Incident Command Center is trained on an exclusive dataset of more than 20,000 major incidents from the insurance industry, data not publicly or commercially available, giving organizations specific and actionable guidance rather than generic advice.
“The time to deploy AI incident response is alongside the AI project rollout – not afterwards and playing catchup,” said Matt Honea, CISO of Hippocratic AI. “AI incident readiness requires playbooks, tabletop exercises, coordinated response and incident reporting, mirroring exactly what cybersecurity teams have built over the last decade. CYGNVS gives organizations an end-to-end platform for managing AI incidents.”
The CYGNVS AI Incident Command Center covers the full lifecycle of Prepare-Practice-Respond-Report.
- Prepare: Organizations enter any AI incident with a playbook already tailored to their industry, geography and incident type, covering bias, model drift, hallucinations, multi-agent mismatch, data leakage and agentic runaway, with step-by-step role-based guidance and fine-grained access control.
- Practice: Teams build muscle memory for AI incidents through tabletop exercises across functions, with After-Action Reports generated automatically to capture learnings and close gaps.
- Respond: When an AI incident escalates, the response does not unravel across disconnected tools. Security teams, legal, executives, outside counsel and AI vendors work from a single secure environment, with every decision logged, timestamped and defensible.
- Report: Pre-built AI regulatory templates cover notification requirements across 56 binding laws and 47 frameworks globally, including EU AI Act, California AI Act, NY Law 144, Colorado AI Act, FDA AI/ML guidelines, so organizations spend less time building forms and more time managing the response.
“Customers have been running over 50 major incidents per week on CYGNVS,” said Arvind Parthasarathi, Founder and CEO of CYGNVS. “When they started facing AI incidents, their teams, executives, and external providers were already on the platform. The AI Incident Command Center is a natural extension of that trust, with purpose-built playbooks, scenarios, and regulatory reporting for a class of incident that didn’t exist a few years ago.”
CYGNVS AI Incident Command Center is generally available. Register for a live AI readiness session on July 16, 2026 with Matt Honea, Hippocratic AI CISO, and Arvind Parthasarathi, CYGNVS Founder and CEO at www.CYGNVS.com/ai-incident.
###
About CYGNVS Inc.
Over 3,000 customer organizations rely on CYGNVS as their Out-of-Band Command Center for cyber and AI incidents, reducing the cost and impact of incidents and outages. Even when systems are unavailable or compromised, AI/security teams, business teams, and external providers collaborate inside CYGNVS to prepare and import response plans, practice in tabletop exercises, successfully execute the response, and report to regulators and customers. CYGNVS AI is trained on an exclusive, growing set of over 20,000 major incidents not accessible publicly or commercially.
Media Contact:
Alyssa Pallotti
APT-PR
alyssa@apt-pr.com
+447397686566